Terraform Module Lifecycle: From First Variable to a Release Teams Can Trust
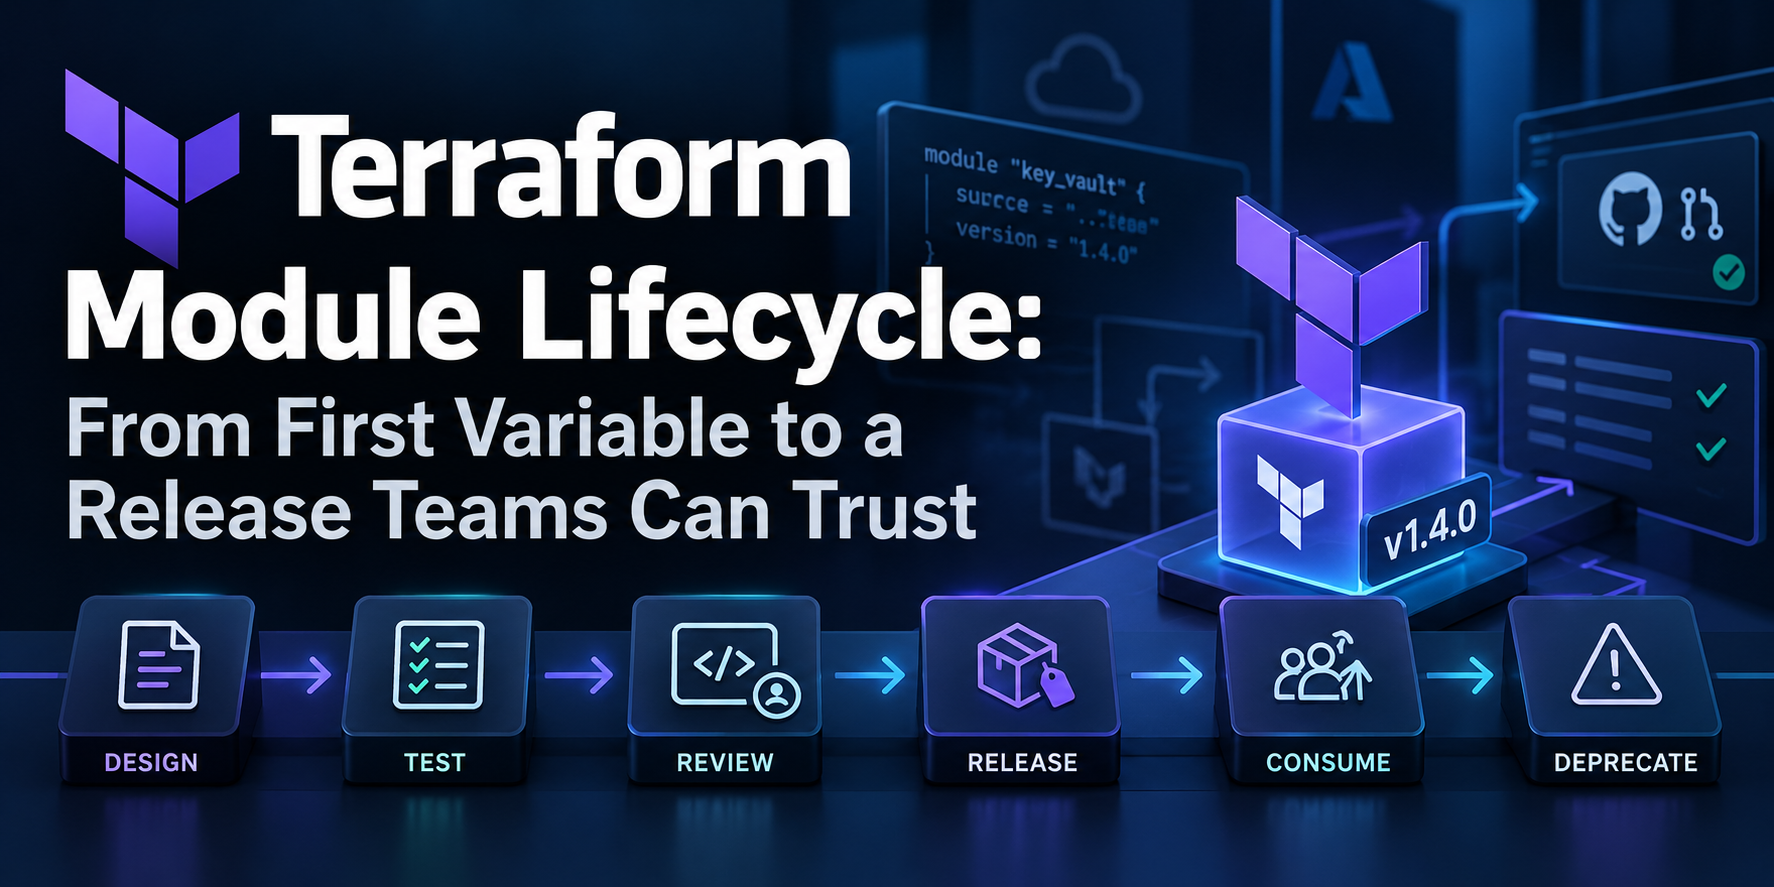
Terraform module lifecycle for platform teams: design, test, review, release, consume and deprecate modules on Azure so every version is one teams can trust.

Terraform module lifecycle for platform teams: design, test, review, release, consume and deprecate modules on Azure so every version is one teams can trust.
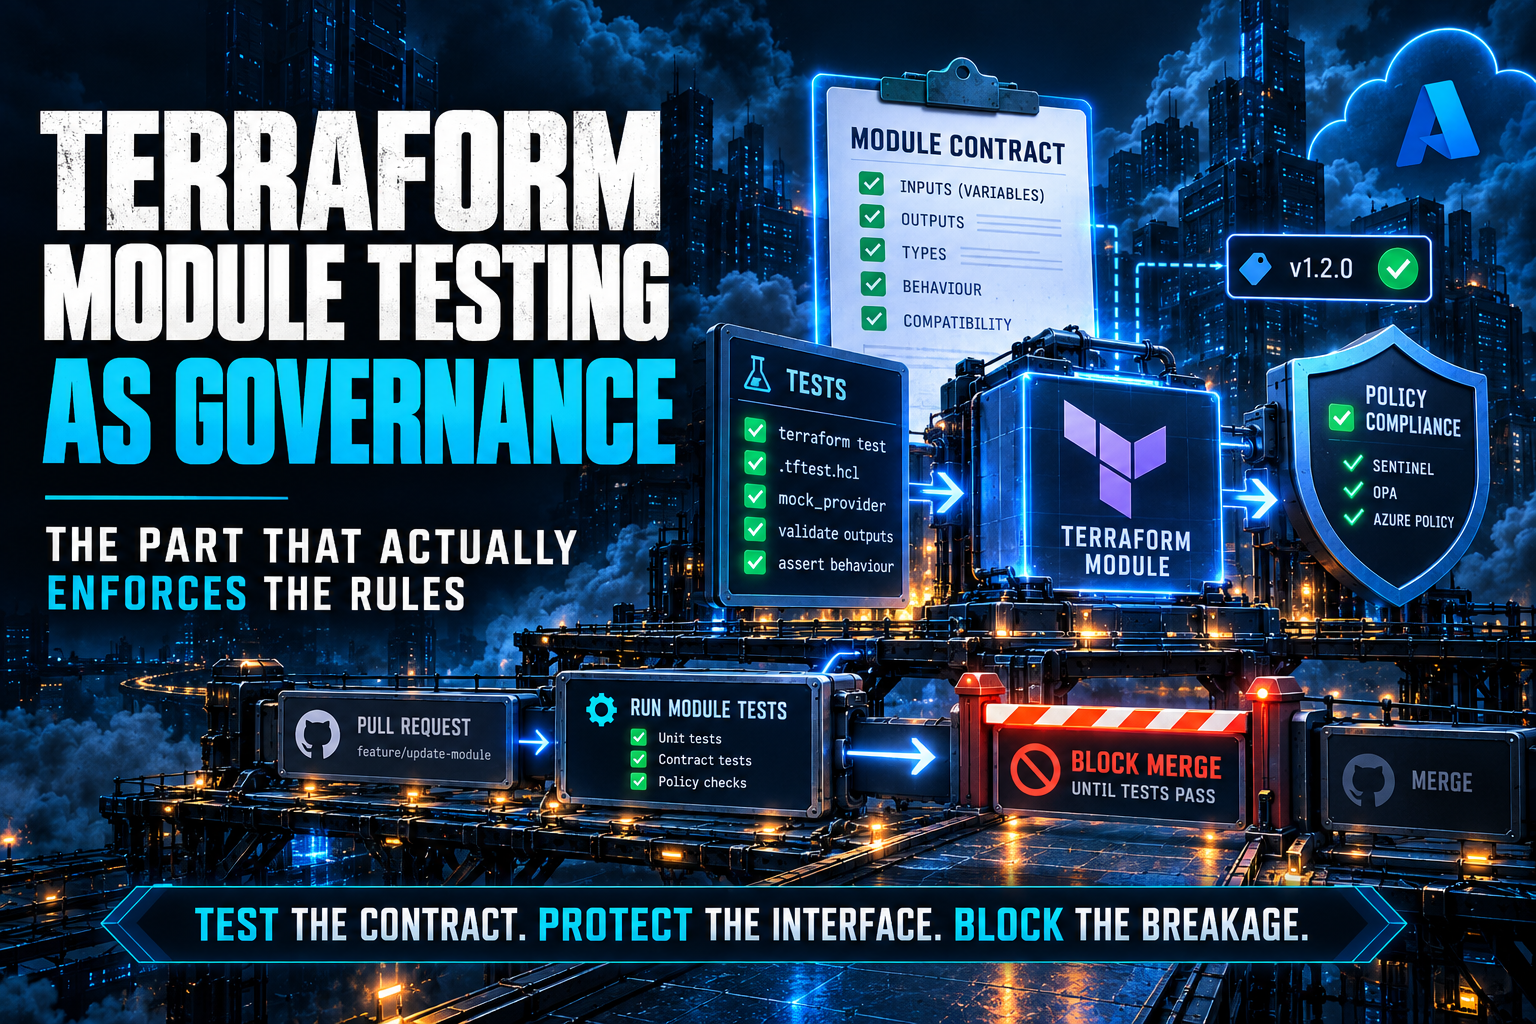
Over the last few weeks this series has built up a fair set of rules. Module boundaries decide what each module is responsible for. Calling conventions decide how those modules get pinned, what goes in and what comes out. Pinned sources, typed inputs, validated variables, outputs treated as a contract, providers passed down rather than … Read more
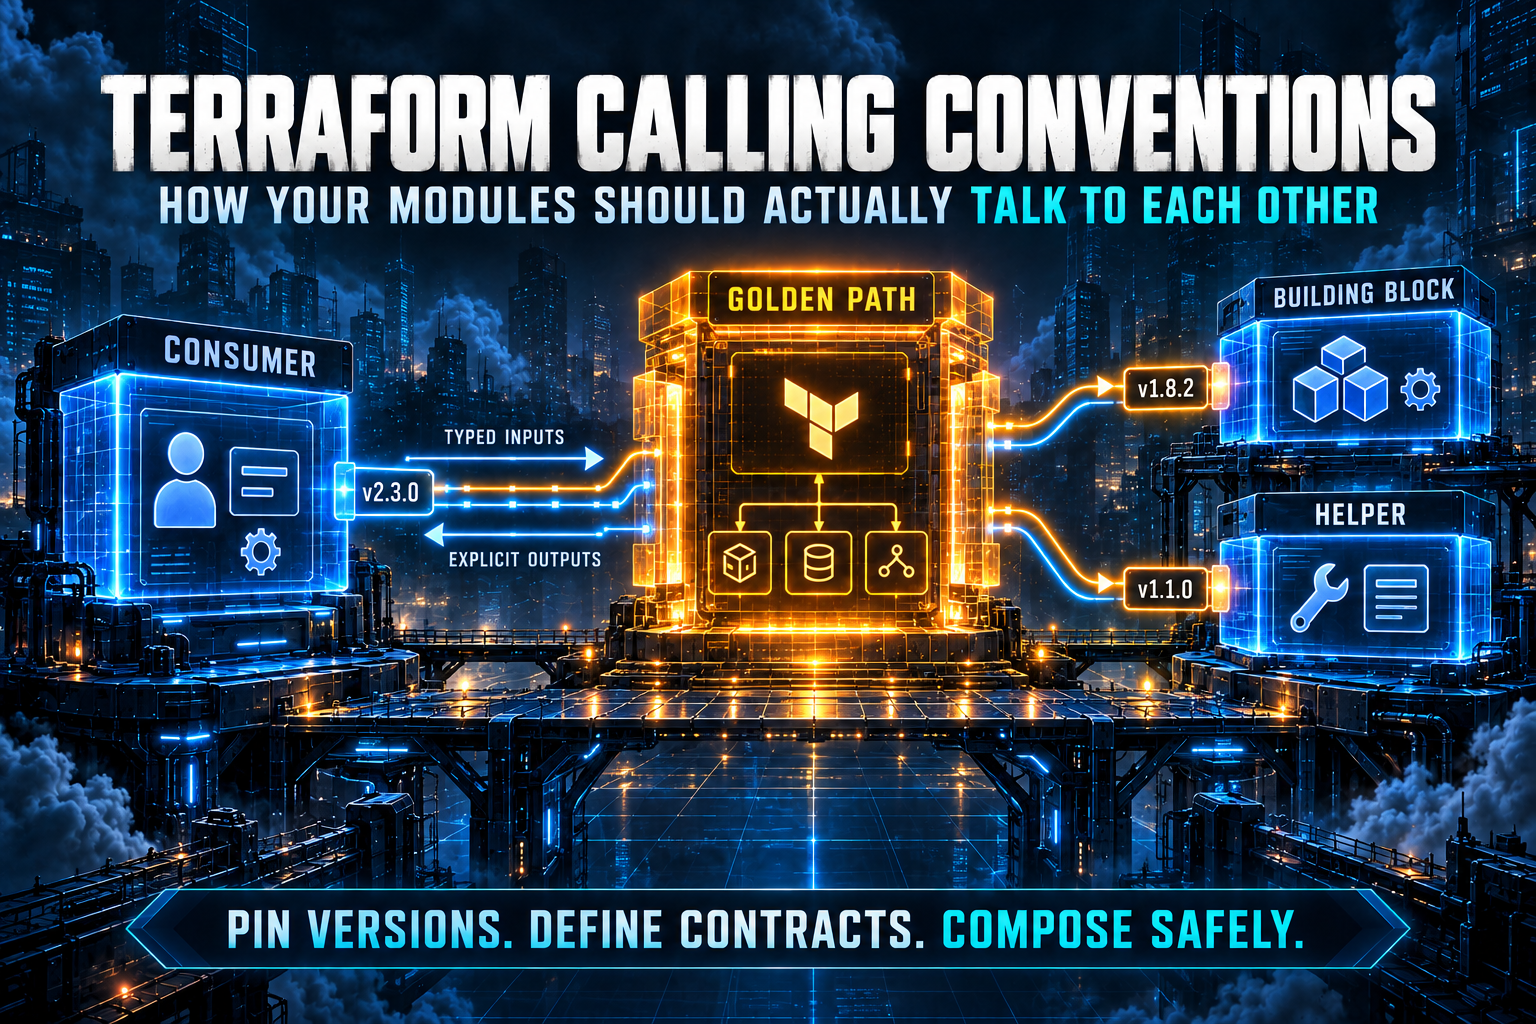
Terraform module source, pinning, inputs and outputs: the calling conventions that let platform teams change modules on Azure without breaking every consumer.
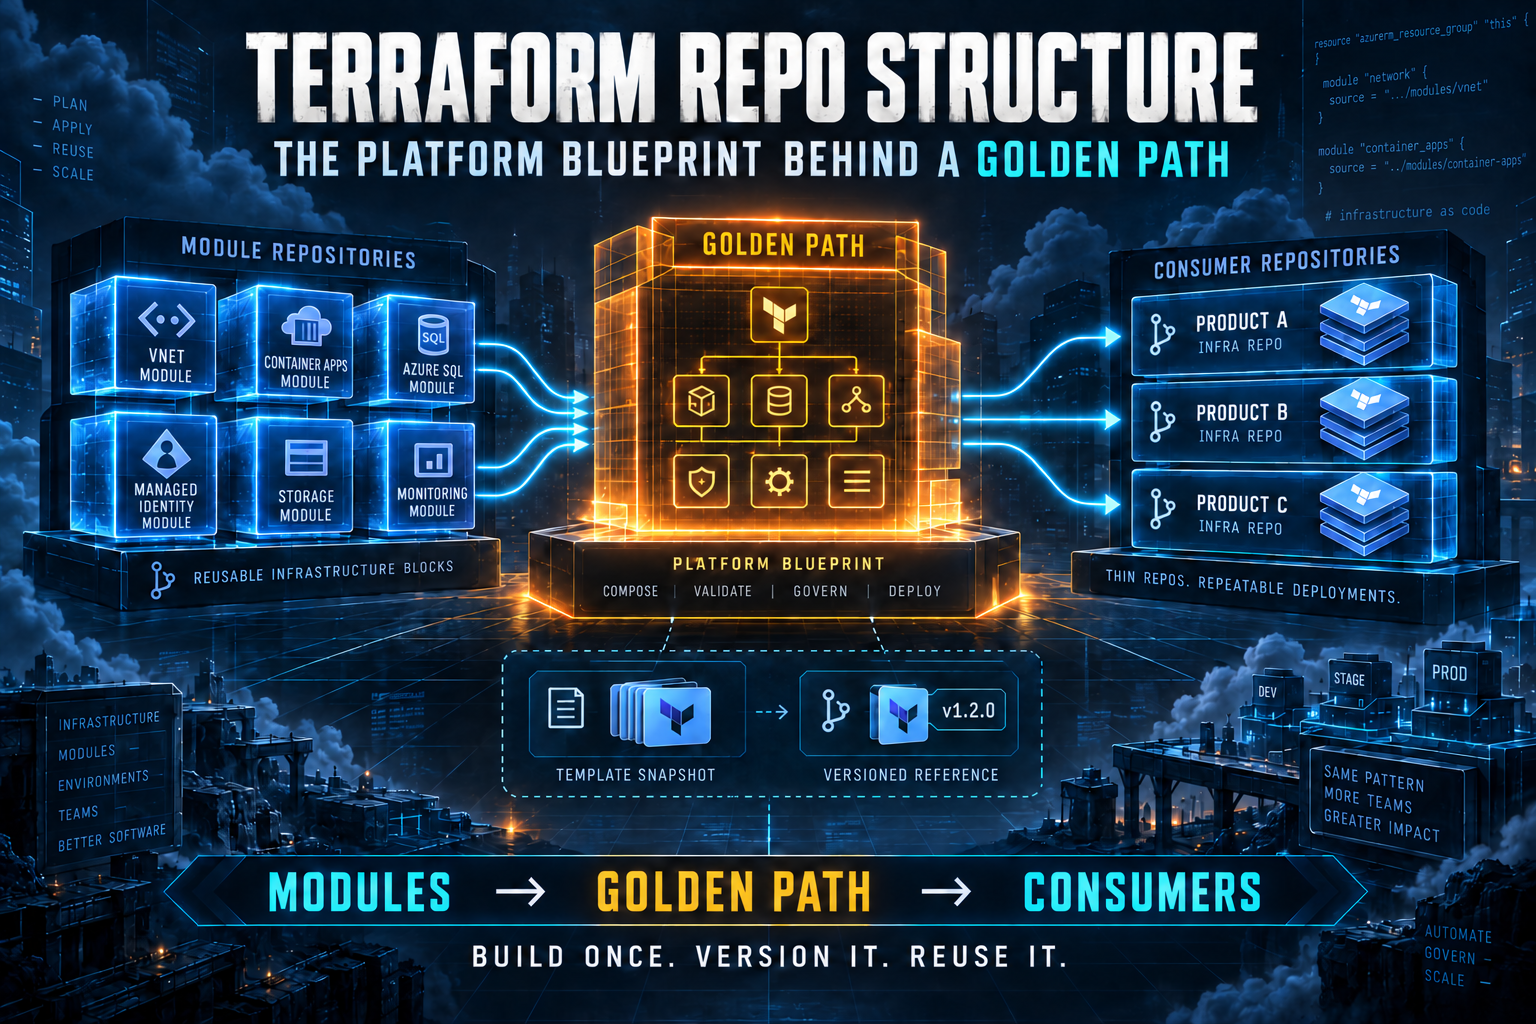
Terraform repo structure explained: how module repos, golden paths, and consumer repos combine to build a governed, reusable Azure platform.
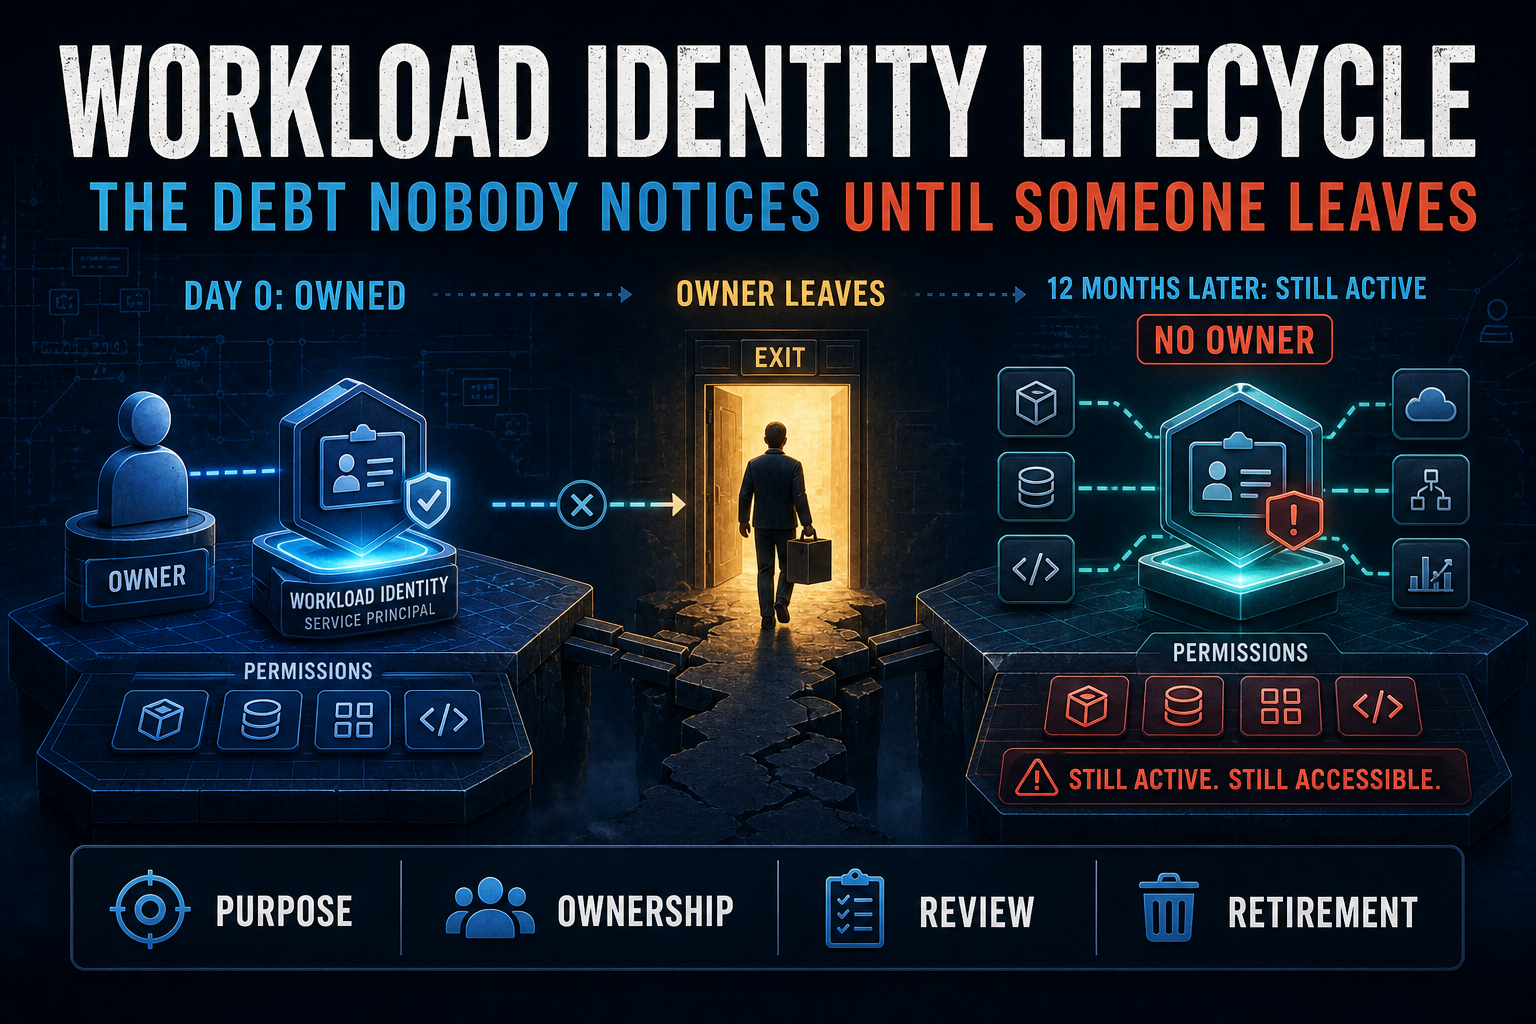
Orphaned service principals and stale secrets don’t announce themselves. What operating workload identity lifecycle in Azure actually requires.
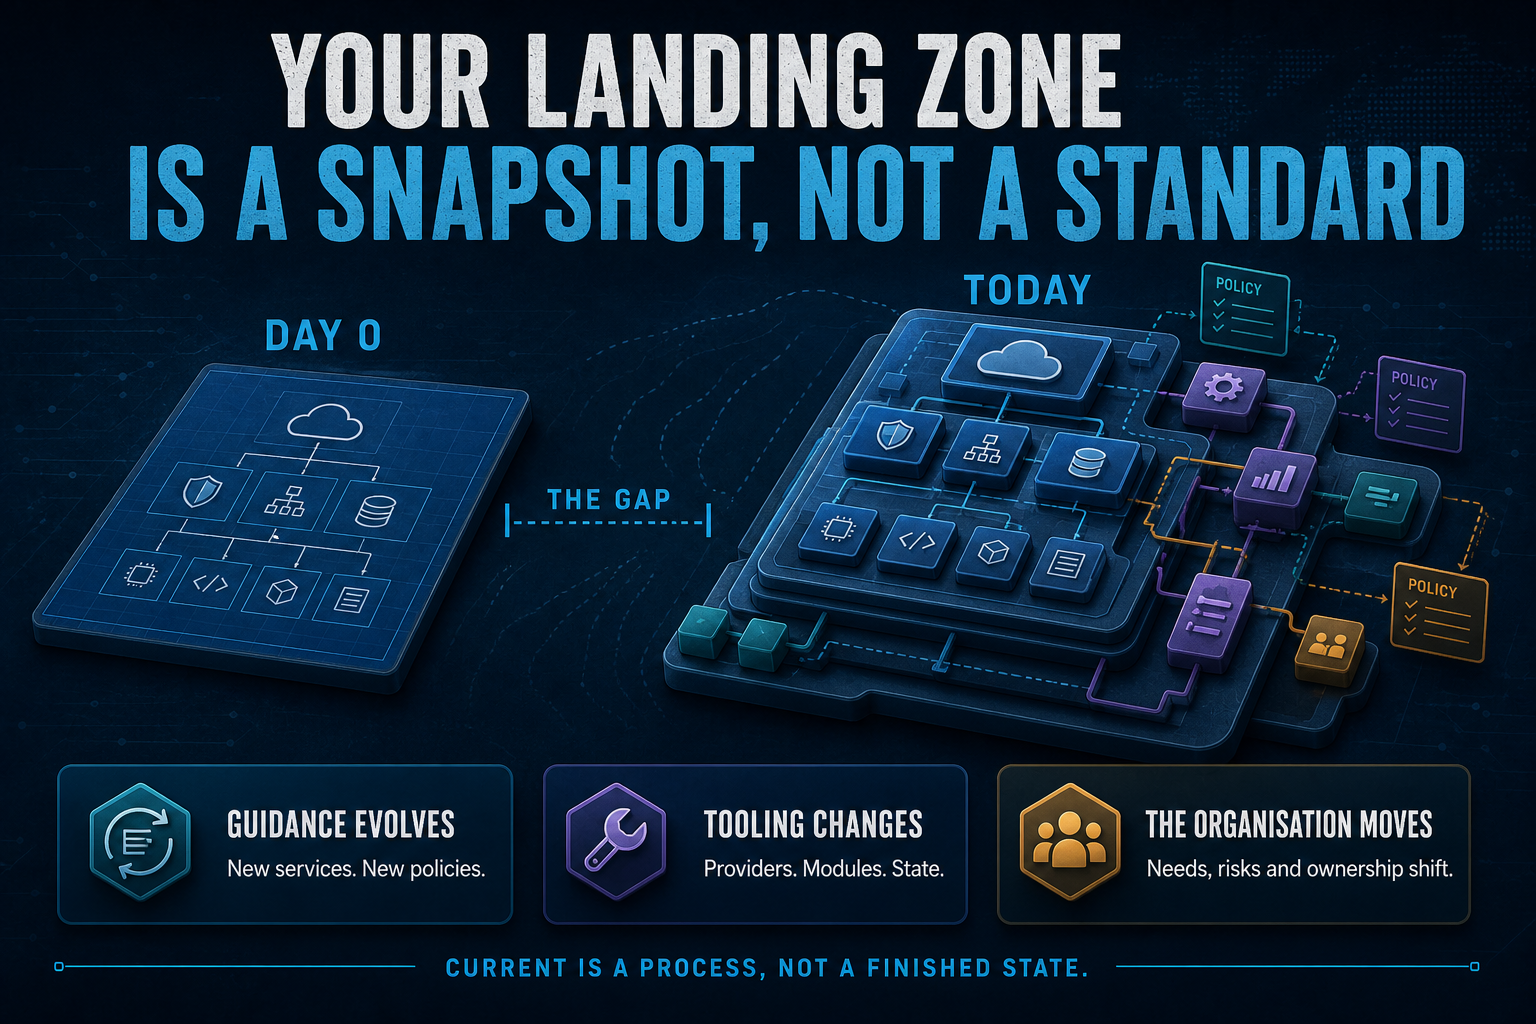
Your Azure landing zone was current the day you deployed it. Since then it’s been drifting. Why landing zone currency is an operating problem, not a one-time build.
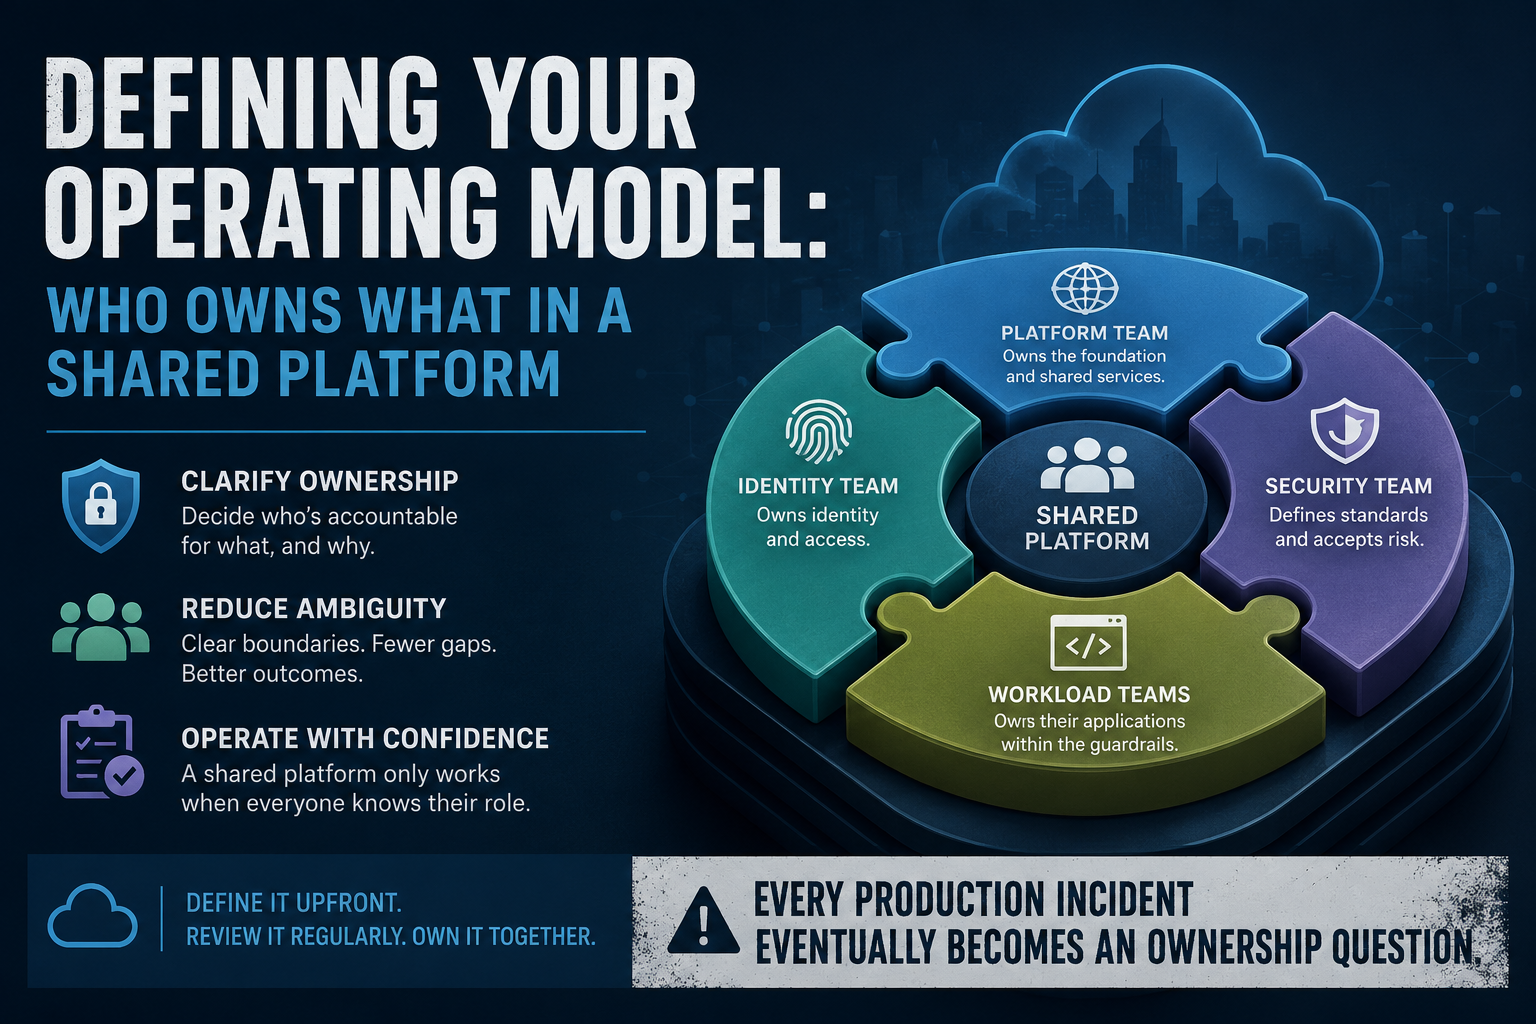
Ownership and access aren’t the same thing. Part 2 of the Azure Platform Operations series: a practical model for who owns what, and why it breaks.
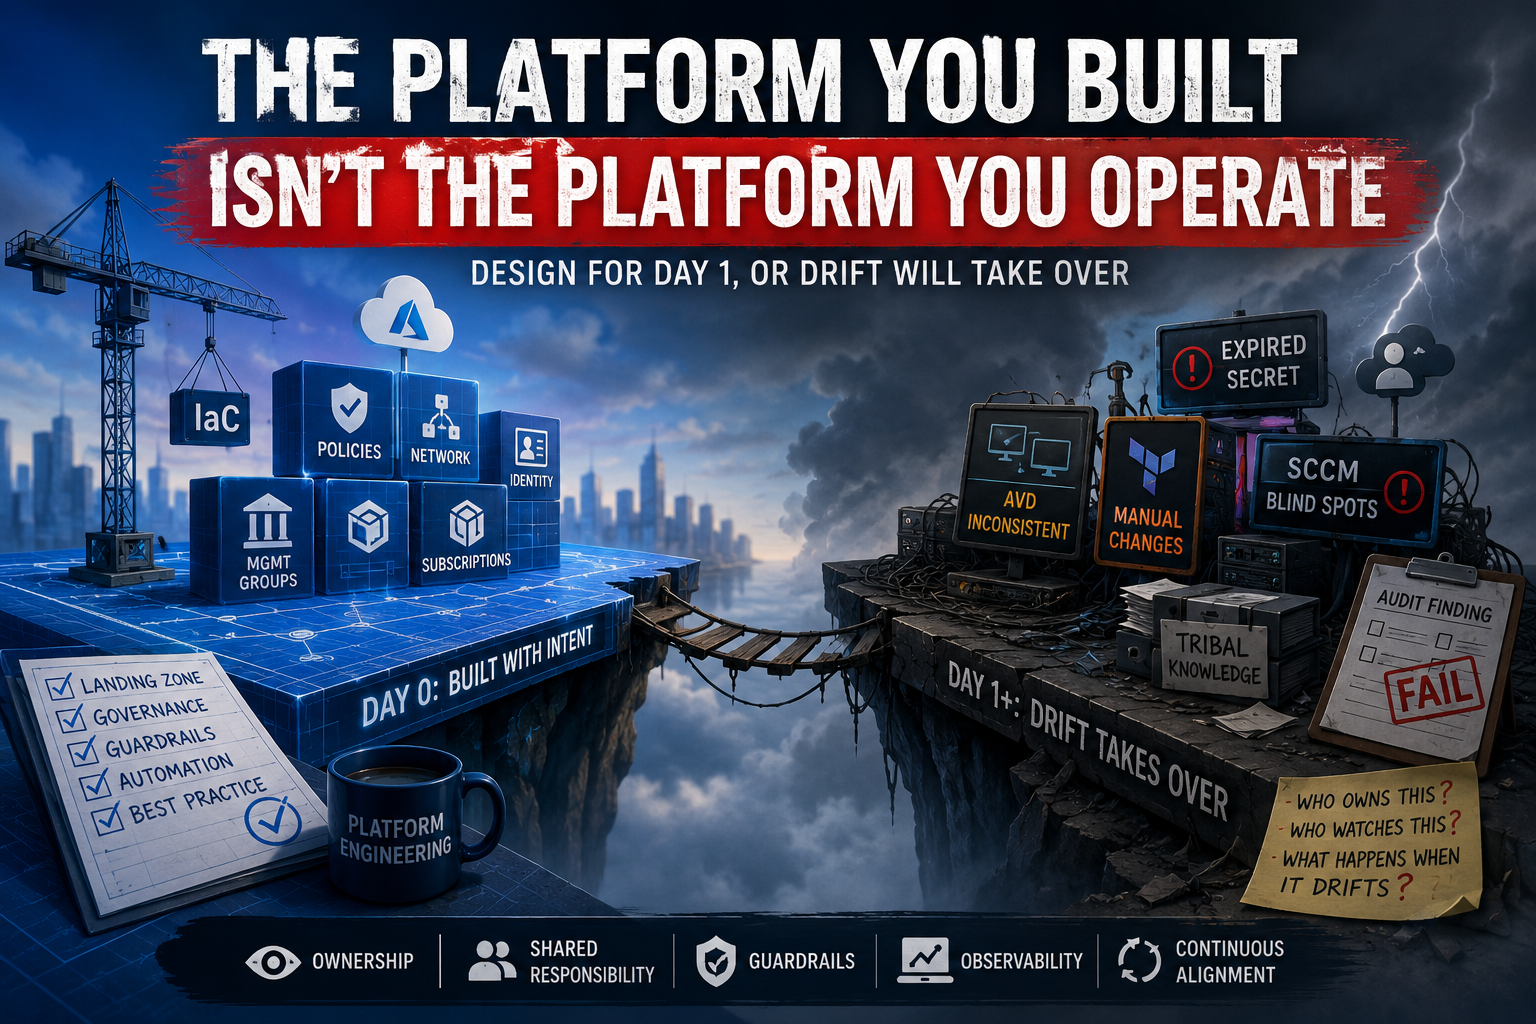
anding zones fail quietly after go-live when nobody owns day 1. Part 1 of the Azure Platform Operations series: service tiers that stop the drift.
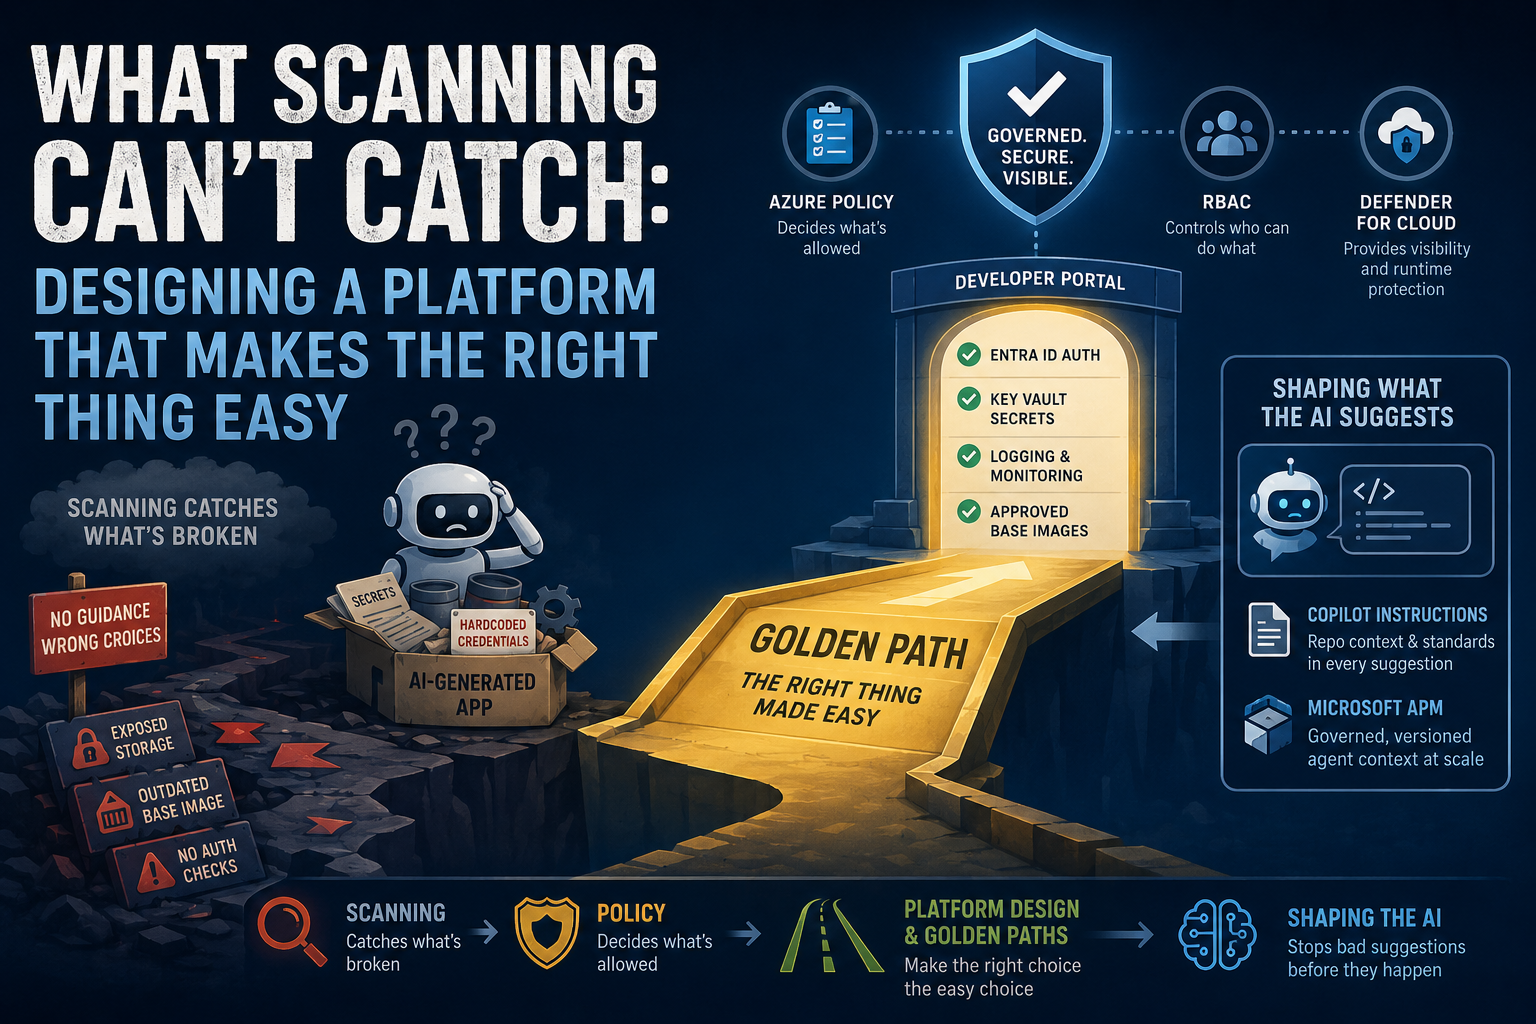
Scanning catches what’s broken. Platform design decides what’s possible. A practical guide to guardrails, golden paths, and AI tooling.
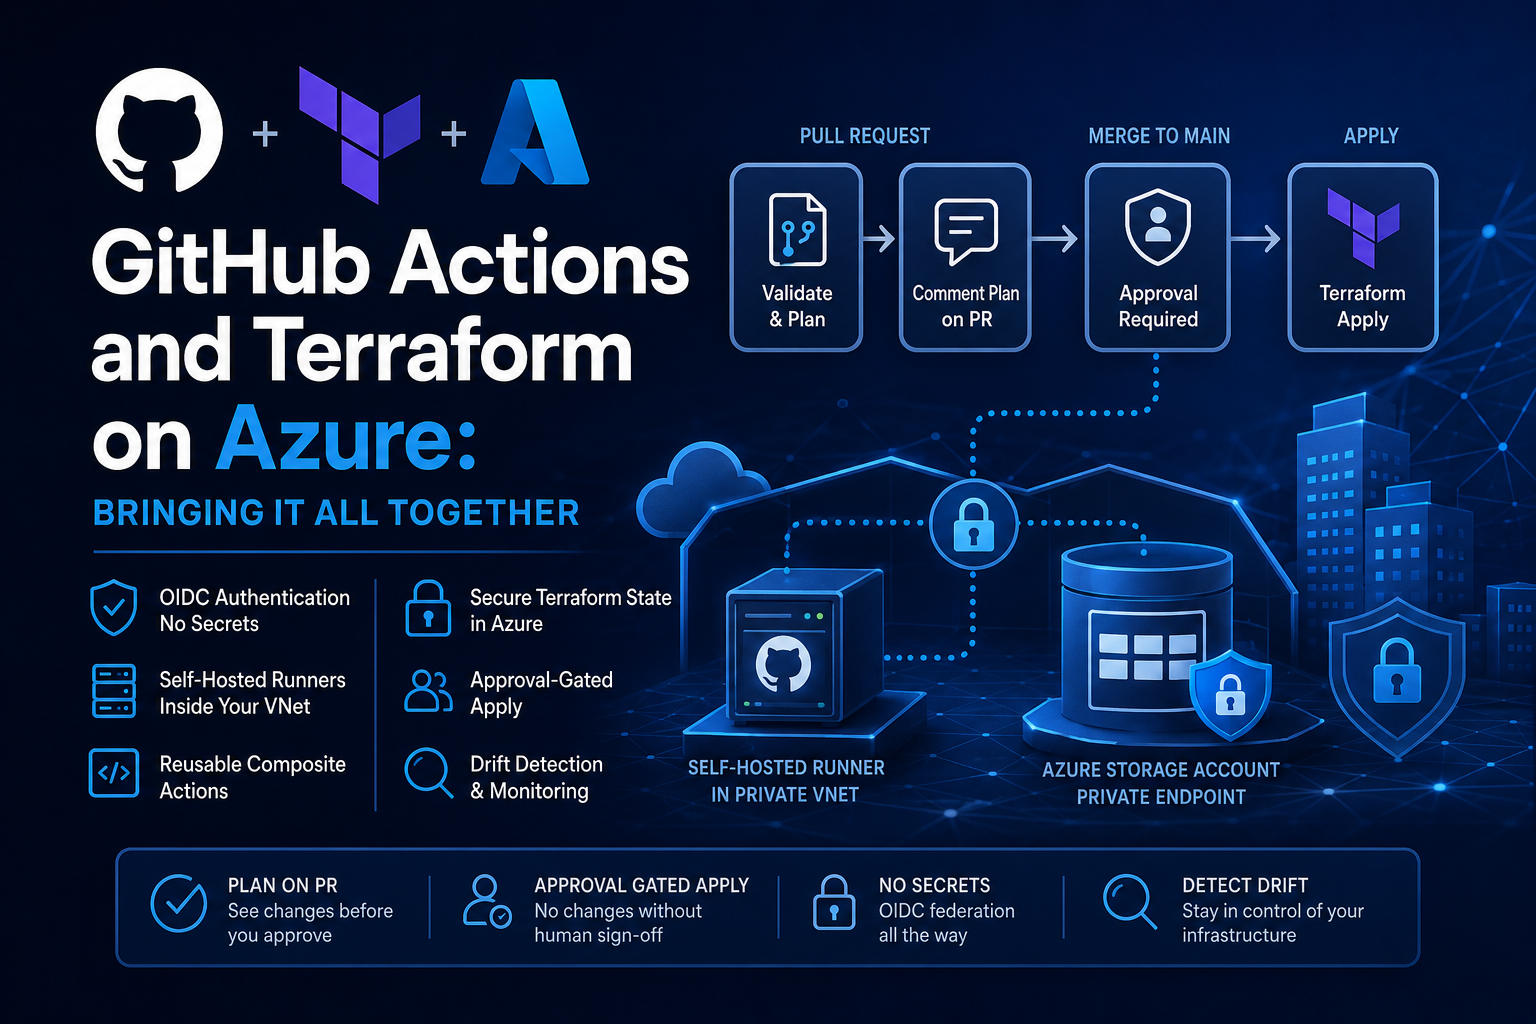
Azure DevOps vs GitHub Actions: a practitioner comparison covering pipelines, templates, federated identity, GitHub Copilot, and when a hybrid approach makes sense